Lifestyle
EU MiCA Transitional Period Ends July 1: Grandfathering Differs by Country, a Pending Application Is Not an Extension
The transitional period in Article 143(3) of the EU's MiCA expired on July 1, 2026. Drawing on ESMA's public statement of June 23, 2026, its statement of April 17, 2026, the list of grandfathering periods decided by each Member State and the official question and answer ESMA_QA_2220, this article sets out what ended, why the grandfathering periods differ from one Member State to another, why a pending application is not an extension, and what ESMA said to providers and to clients.
About 14 min read
The transitional period set out in Article 143(3) of the EU's Markets in Crypto-Assets Regulation (MiCA) expired on July 1, 2026. In its statement of April 17, 2026, the European Securities and Markets Authority (ESMA) wrote that the MiCA transitional period would officially expire across the EU on that date, and in its public statement of June 23, 2026 it set out how crypto-asset service providers (CASPs) without an authorisation should wind down in an orderly manner.
This article was checked on September 17, 2026, the day all four ESMA documents were fetched again and read through: the two statements above, ESMA's list of the grandfathering periods decided by each Member State under Article 143, and the official question and answer ESMA_QA_2220. We have tested nothing ourselves and we give no investment or legal advice; every sentence here is limited to what those four documents print, and figures that move, such as how many firms appear on ESMA's register, are left out entirely.
What ended on July 1: the last day of the old regime's grandfathering
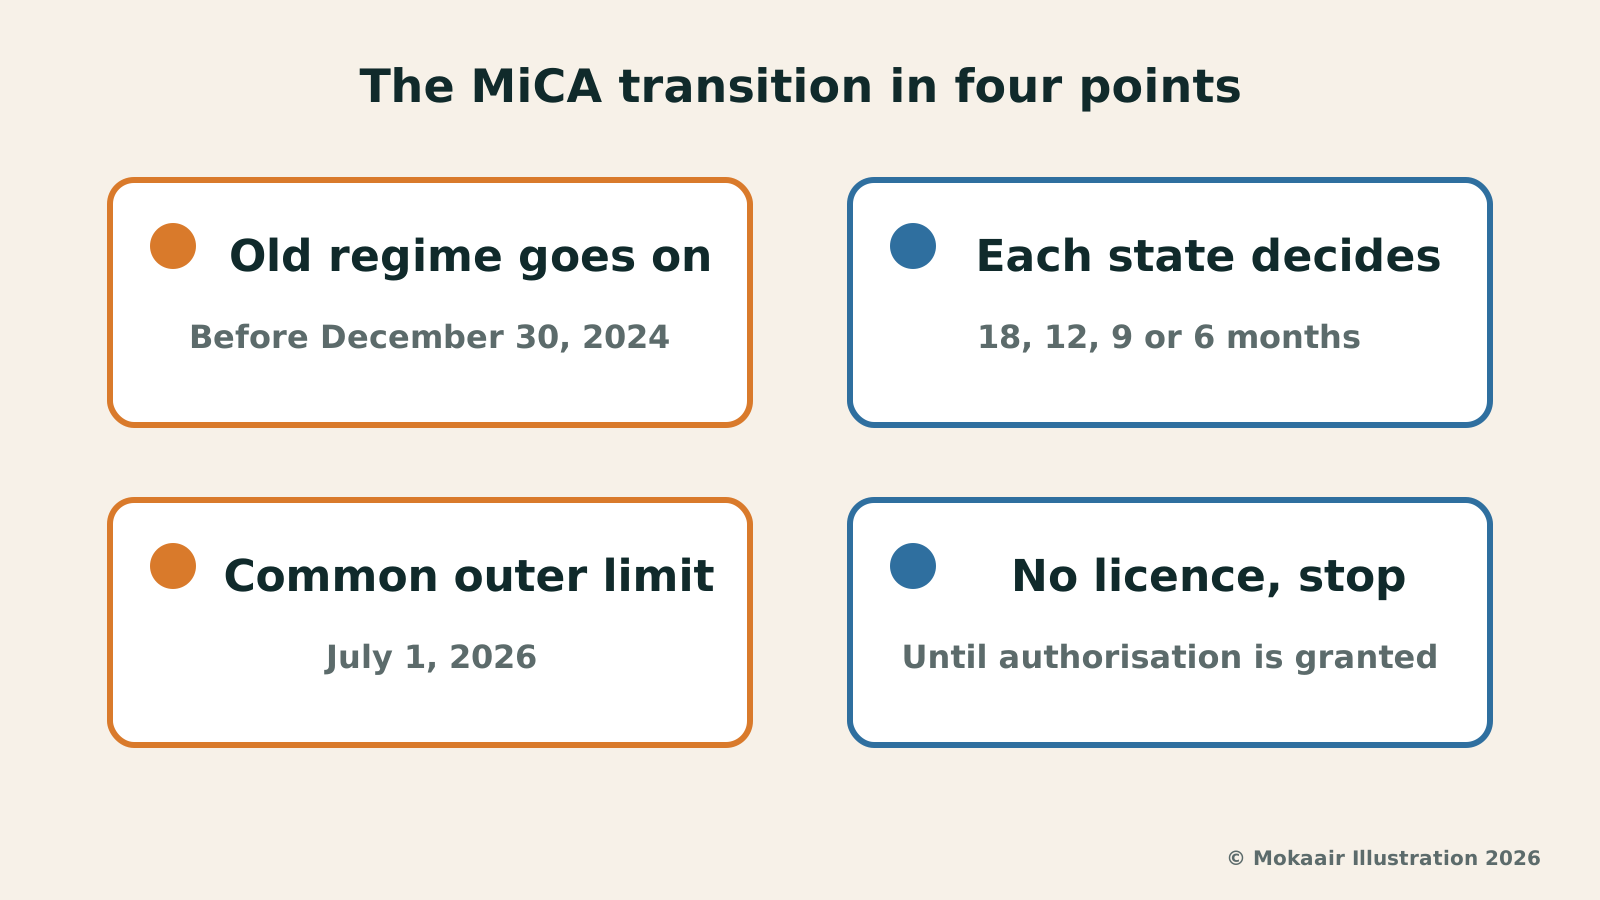
The first subparagraph of Article 143(3) provides that crypto-asset service providers that provided their services in accordance with applicable law before December 30, 2024 may continue to do so until July 1, 2026, or until they are granted or refused an authorisation pursuant to Article 63, whichever is sooner. That subparagraph is what is usually called grandfathering: a provider already operating under the old regime could carry on for the time being, without having to stop and wait for a MiCA licence.
The April 17 statement is explicit: the MiCA transitional period will officially expire across the EU on July 1, 2026, and after that date any entity providing crypto-asset services to EU clients without a MiCA licence will be in breach of EU law and must cease offering such services. A footnote adds that this applies irrespective of whether MiCA has been implemented in a Member State or not. Footnote 4 of the same statement points out that two categories of entities were not permitted to provide services even before July 1: first, entities that did not provide crypto-asset services in accordance with applicable national law before December 30, 2024 and therefore could not rely on the transitional regime; and second, entities active in Member States where the transitional period had already ended before July 1, 2026.
Each Member State decided the length for itself
Why do the countries differ? The second subparagraph of Article 143(3) hands the choice to the Member States: they may decide not to apply the transitional regime provided for in the first subparagraph, or to reduce its duration, where they consider that their national regulatory framework applicable before December 30, 2024 is less strict than this Regulation. The third subparagraph requires Member States to notify the Commission and ESMA by June 30, 2024 whether they have exercised that option and how long the transitional regime is. ESMA itself issued a document listing each country's length, and that is the document used here.
Counting row by row through the version of that list obtained on the day of this check (the PDF's internal modification time is May 19, 2026): the Member State column holds 27 rows, and the lengths come in four values, 18 months in 15 countries, 12 months in 5 (Germany, Ireland, Lithuania, Austria and Slovakia), 9 months in Sweden alone, and 6 months in 6 (Latvia, Hungary, the Netherlands, Poland, Slovenia and Finland). Three European Economic Area (EEA) countries are listed in a separate block: Iceland and Liechtenstein at 18 months, Norway at 12 months. The wording of the April 17 statement is "across the EU"; checking these four documents up to September 17, 2026, we saw no statement of an end date for those three countries.
Two things about this list need care. First, it gives months only, with no start date and no expiry date for any country; a date obtained by adding those months to December 30, 2024 is the reader's own arithmetic, not something ESMA prints. Second, the general footnote itself says that some of these periods were communicated to ESMA by national competent authorities and reflect their expectations at the time, and some of them may not have been incorporated into national law yet. Four further countries, Bulgaria, the Czech Republic, Denmark and Italy, each carry a footnote of their own, and what those footnotes state is an application deadline rather than a length of grandfathering.
| Grandfathering period | EU Member States | EEA countries listed separately |
|---|---|---|
| 18 months | 15 countries | Iceland, Liechtenstein |
| 12 months | 5 countries | Norway |
| 9 months | 1 country (Sweden) | None |
| 6 months | 6 countries | None |
Grandfathering is not protection: no authorisation, no MiCA safeguards
The phrase most easily misread is "application pending". ESMA's official question and answer ESMA_QA_2220 (answer dated July 4, 2024, on the basis of Article 143(3)) asks exactly that: where an entity has applied but has been neither granted nor refused authorisation by the end of the transition period, can it continue providing services? The answer is that where an entity has not been authorised as a CASP by the end of the transition period applicable in the relevant Member State, they must cease providing crypto-asset services until they are granted authorisation as a CASP under MiCA.
The scope of protection needs separating out too. The June 23 statement reminds clients of unauthorised providers that, whether the entity is an EU or a non-EU one, they do not benefit from MiCA safeguards, including protections for client assets; providers established outside the EU also cannot provide MiCA services to EU clients or solicit EU clients, and this applies in a business-to-business context as well, except under the narrow reverse solicitation regime, where services are strictly provided at the client's own exclusive initiative. The April 17 statement goes further into detail: MiCA protections only apply to the specific authorised legal entity in the EU, not to other companies of the same group and not to non-EU entities; a provider may operate under the same brand across multiple companies or countries, so what matters is which entity the contract shows as actually providing the service.
How ESMA requires unauthorised providers to wind down
The June 23 statement says that while a number of providers will have obtained authorisation by the deadline, other entities, including significant providers currently servicing EU clients under national regimes, may not be authorised by then. The statement lists three things unauthorised providers must do: immediately stop onboarding new EU clients, refrain from opening new client relationships or accounts, and cease marketing activities and solicitation; limit the provision of services to actions necessary to sell or transfer crypto-assets, reallocate assets or close positions, with custody of clients' crypto-assets continuing only for the period strictly necessary to complete an orderly exit; and communicate clearly, promptly and repeatedly with retail and institutional clients about the measures taken to safeguard their assets and the wind-down plans, communications that should include a deadline by which any residual positions would be closed automatically and information about client protection requirements.
The April 17 statement adds what ESMA expects of a wind-down plan: that it enable an orderly exit without causing undue economic harm to clients, including by arranging the offboarding of clients (for example by transferring their crypto-assets to a provider that holds an authorisation, or to a self-hosted wallet); that providers should give existing clients prior notice before implementing the wind-down plan; and that plans should be operational, credible and immediately executable. ESMA also states that by July 1, 2026, when the transitional period ends across the EU, any unauthorised provider must have implemented its wind-down plan.
The other half of the picture is the providers that are authorised: the April 17 statement expects them to actively manage the migration of existing clients ahead of July 1, 2026, and to onboard existing EU clients before the end of the transitional period; what that same statement expects of the national competent authorities is to verify the existence and adequacy of orderly wind-down plans and ensure they are implemented in a timely manner, to take action against the unauthorised provision of crypto-asset services following the end of the transitional period (in cooperation with other competent authorities where appropriate), and to scrutinise client migration strategies. The June 23 statement says wind-down arrangements should be implemented in compliance with all relevant EU or national conduct laws and with anti-money laundering and countering the financing of terrorism (AML/CFT) obligations, including customer due diligence, transaction monitoring and screening against sanctions lists; within the ESMA cooperation framework, national competent authorities may, where necessary, take coordinated action against unauthorised providers after the transitional period.
What users can do: work out which entity you are dealing with
What ESMA says to clients sits in two places: the June 23 statement invites clients using crypto-asset services in the EU to verify on ESMA's register whether their provider is authorised under MiCA, and to act promptly where this is not the case, including by transferring their crypto-assets to a provider that holds an authorisation, where one is identified, or to a self-hosted wallet. The April 17 statement gives three steps: check that the company you are using is listed as authorised in ESMA's Interim MiCA Register, work out who you are dealing with, and act if you need to. ESMA also states that staying with an unauthorised provider may mean less legal protection and a greater risk of losing access to your assets.
Both statements speak of EU clients. Checking these four documents up to September 17, 2026, we saw nothing about non-EU residents, readers in Taiwan for instance, using EU providers, and no provider named. What follows is an example designed by the editors, not something we tested: someone holds an account on a platform registered in an EU Member State and wants to know whether they are about to be cut off. On ESMA's account, the thing to do is to establish which legal entity the contract is with, and then check that entity's status on the register, rather than going by the brand.
Frequently asked questions
Did the EU only begin regulating crypto-assets after July 1, 2026?
No. What Article 143(3) of MiCA granted was a buffer: crypto-asset service providers that provided their services in accordance with applicable law before December 30, 2024 could continue to do so until July 1, 2026, or until they were granted or refused an authorisation pursuant to Article 63, whichever was sooner. July 1 is the common outer limit of that buffer, not the first day the rules took effect.
A provider has filed its application and it is still under review. Can it keep operating?
Under ESMA's official question and answer ESMA_QA_2220, an entity that has not been authorised as a CASP by the end of the transition period applicable in the relevant Member State must cease providing crypto-asset services until it is granted authorisation as a CASP under MiCA. The same answer also says such an entity should apply as early as possible, so that national competent authorities have time to assess the application without disrupting its services.
Is the deadline the same in every Member State?
No. Counting row by row through the version of ESMA's list obtained on the day of this check, the 27 EU Member States have four lengths of grandfathering between them: 18 months, 12 months, 9 months and 6 months, with July 1, 2026 as the common outer limit. Footnote 4 of the April 17 statement also points out that entities active in Member States where the transitional period had already ended before July 1, 2026 were not permitted to provide crypto-asset services even before that date.
How do I check whether a provider holds a MiCA authorisation?
In both statements ESMA leaves this to clients themselves: verify on ESMA's register whether your provider is authorised under MiCA, and the April 17 statement asks readers to check before they invest or transfer funds. Note that what you check is a legal entity, not a brand. MiCA protections only apply to the specific authorised legal entity in the EU, not to other companies of the same group and not to non-EU entities.
When a provider winds down, are clients told first?
That is what ESMA expects. The April 17 statement says providers should give existing clients prior notice before implementing the wind-down plan; the June 23 statement requires clear, prompt and repeated communication with clients, which should include a deadline by which any residual positions would be closed automatically. Providers set that deadline themselves: checking these four documents up to September 17, 2026, we saw no single date set by ESMA.
Do Iceland, Liechtenstein and Norway also end on July 1?
The documents do not say so. ESMA's list places these three European Economic Area countries in a block separate from the 27 EU Member States (Iceland 18 months, Liechtenstein 18 months, Norway 12 months), while the wording of the April 17 statement is "across the EU". Checking these four documents up to September 17, 2026, we saw no statement of when the transitional period ends in those three countries.
Are users in Taiwan affected?
Both ESMA statements speak of EU clients. Checking these four documents up to September 17, 2026, we saw nothing about non-EU residents using EU providers and no provider named, so this article draws no inference. Taiwan's own regime is a separate subject that this article does not go into; the second link at the end of this article is that story.
2026 Crypto News Roundup: Key Developments in Regulation, Technology and Industry2026 Crypto News Roundup: Key Developments in Regulation, Technology and IndustryThis site's 2026 crypto news explainers, in six jurisdictions — Taiwan, the US, the UK, the EU, Japan, South Korea: the Virtual Asset Service Act, the proposed GENIUS Act rules, the joint SEC–CFTC interpretation and the SEC's own proposal, the end of MiCA's transitional period and its link to the payment rules, the FCA's perimeter guidance, Japan's FSA reports and South Korea's manipulation referrals. Regulation, technology and industry only, no prices, with official sources and a check date.Read the full article
Taiwan's Virtual Asset Service Act Clears Third Reading: Seven Kinds of Provider, Stablecoin Licensing, No Commencement Date YetTaiwan's Virtual Asset Service Act Clears Third Reading: Seven Kinds of Provider, Stablecoin Licensing, No Commencement Date YetOn June 30, 2026 Taiwan's Legislative Yuan passed the Virtual Asset Service Act (虛擬資產服務法) on third reading, and its 56 articles were promulgated on July 22, 2026. Working from the Financial Supervisory Commission's press release and two official legal databases, this article sets out the seven kinds of virtual asset service provider, licensing kind by kind, the reserve-asset rules for stablecoins, and why the 12- and 21-month transition periods in article 55 have not started running.Read the full article
Lifestyle
EBA Opinion as the PSD2 Transition Period for E-Money Tokens Ends: Three Scenarios, Four Conditions
On February 12, 2026, the European Banking Authority published Opinion EBA/OP/2026/01, setting out what national competent authorities are advised to do once the transition period in its No-Action Letter ends on March 2, 2026. Working from the Opinion and the No-Action Letter themselves, this article explains the three scenarios, the four conditions and the two restrictions, and why this is advice rather than a rule that takes direct effect on firms.
Lifestyle
Brazil's Petrobras tests Cardano blockchain to track claims about cleaner jet fuel and diesel
According to CoinDesk, Brazil's state-owned energy company Petrobras is testing the Cardano blockchain in two research projects: one to stop the same emissions cut from sustainable aviation fuel being counted twice, the other to record the history of its partly renewable Diesel R. Both are still research work, with no timeline for wider use.
Lifestyle
Cboe and S&P Dow Jones Indices extend their S&P 500 options deal to 2051 and leave the door open to tokenized options
According to CoinDesk, exchange operator Cboe and index provider S&P Dow Jones Indices have extended Cboe's exclusive right to offer S&P 500 options by 25 years, to 2051. The deal says they may explore blockchain-based 'tokenized' options, but no product, timeline or details were announced. Here is what that means and what it does not.
Lifestyle
SEC Charges Two Groups of Entities Allegedly Behind Crypto Frauds Using WhatsApp and "AI Trading" Claims
On September 29, 2026, the US SEC charged two groups of entities, Cryptoaiml and TSAI, alleging they defrauded hundreds of individual investors, many in the US. The SEC says they falsely claimed to be SEC-regulated and used AI trading signals and bots as bait in schemes totaling at least $15 million. Here is what the SEC alleges and the warning signs readers can watch for.
Articles that cite this one
- UK FCA Publishes Final Cryptoasset Perimeter Guidance PS26/18: Applications Open September 30, New Regime Takes Effect October 2027
- Taiwan's Virtual Asset Service Act Clears Third Reading: Seven Kinds of Provider, Stablecoin Licensing, No Commencement Date Yet
- 2026 Crypto News Roundup: Key Developments in Regulation, Technology and Industry
Latest travel guides

GuideTokyo
Where to Stay in Tokyo: Comparing Shinjuku, Ueno, Tokyo Station, Shibuya, Asakusa, Ikebukuro, and Ginza, Plus Airport Access, Accommodation Tax, and Luggage Delivery
Where should you stay in Tokyo? Compare Shinjuku, Ueno, Tokyo Station, Shibuya, Asakusa, Ikebukuro, and Ginza by the same criteria: access from Narita and Haneda, transit routes, nearby attractions, neighborhood character, and who each area suits. Includes a comparison table, a Yamanote Line diagram, Tokyo’s accommodation tax as verified in 2026/9 (changing to 3% in 2027/4), and Airport TA-Q-BIN luggage shipping rules.
- Budget
- Hotels

GuideTokyo
How to Choose Tokyo Transit Passes: Are Suica, Welcome Suica, the Tokyo Subway Ticket, and the JR Pass Worth It?
On a first Tokyo trip, start with an IC card and pay per ride (Welcome Suica has no deposit and is valid for 28 days). If you take four or more subway rides in a day, add a 72-hour Tokyo Subway Ticket for 2,000 yen; a JR Pass is never worthwhile if you stay in Tokyo and do not go to Kansai. See what TOURIST PASMO, Suica on iPhone, and the Tokyo Metro day pass do and do not cover, with a decision chart. Prices verified in September 2026.
- Transport
- Budget

GuideTokyo
Tokyo Disneyland and DisneySea Guide: Ticket Prices, Fantasy Springs, Disney Premier Access (DPA), Standby Pass, and Which Park to Choose for Your First Visit
Tokyo Disney one-day Passport prices vary: most weekdays in 9/2026 cost ¥9,900 and weekends ¥10,900. At 14:00 daily, tickets go on sale for the same date two months later. Free Priority Pass is no longer on the official service list; only paid Disney Premier Access (¥1,000–3,500 per person per use) shortens waits. Covers hours, the 25th anniversary, Standby Pass, Entry Request, Fantasy Springs access and first-visit park choice; checked on the official site in 9/2026.
- Itineraries
- Family
Sources
- ESMA public statement: MiCA transitional period ends, ESMA requires unauthorised crypto-asset service providers to wind down in an orderly manner (ESMA75-113276571-1710, June 23, 2026) · Checked:
- ESMA Statement on the end of transitional periods under MiCA (ESMA75-113276571-1679, April 17, 2026) · Checked:
- ESMA: List of grandfathering periods decided by Member States under Article 143 of the Markets in Crypto-Assets Regulation (MiCA) · Checked:
- ESMA official question and answer ESMA_QA_2220: Entities not authorised as CASPs by the end of the transition period · Checked: