Synology Advisory SA-26:13: Two Unauthenticated 9.8 Flaws — Check Your Version Before Updating
At 4:17 PM Taipei time on September 18, 2026, Synology published security advisory Synology-SA-26:13, addressing eight CVE entries in DSM — two rated Critical with a CVSS 3.1 score of 9.8, exploitable without authentication. The advisory's Mitigation field reads None. Here are the fixed releases for each branch and how to check your NAS's current version yourself (verified September 2026).
News date: About 11 min read
Contents
At 4:17 PM Taipei time on September 18, 2026, Synology published security advisory Synology-SA-26:13 DSM, addressing vulnerabilities in DSM (DiskStation Manager, the operating system for Synology NAS devices). This advisory's overall severity is Critical and its status is Resolved. Of the eight CVE entries the advisory lists, two are rated Critical by Synology with a CVSS 3.1 base score of 9.8, and belong to the group exploitable by remote attackers without authentication. The fix is to upgrade DSM to at least the fixed release for each branch, or above.
The data in this article was verified on September 26, 2026, drawn from Synology's SA-26:13 advisory page, the two CVE records (CVE-2026-13684 and CVE-2026-13639, including the assessment CISA added), and the DSM release notes. This site has not tested this itself and does not offer workarounds; where an answer could not be found, that is stated directly.
What the September 18 Advisory Says
The advisory's formal name is Synology-SA-26:13 DSM, published at 4:17 PM Taipei time (UTC+8) on September 18, 2026, with the same Last Updated time; the Revision table at the bottom of the page shows only Revision 1, also dated September 18. As checked on the advisory page through September 26, 2026, the advisory had not been revised; if it is revised later, readers can check the page's own Last Updated field and Revision table.
The advisory groups the eight CVEs into three sets. CVE-2026-13684, CVE-2026-13639, and CVE-2026-13635 can be exploited by remote attackers without authentication; the consequences vary by CVE and may include reading or writing arbitrary files, causing denial of service, or obtaining non-sensitive information. CVE-2026-13673, CVE-2026-6205, and CVE-2026-13666 require an authenticated remote user, with one of them occurring only if the victim clicks a sharing URL. CVE-2026-13623 and CVE-2026-13683 require an authenticated user with administrator privileges, with consequences limited to reading or writing limited files or obtaining non-sensitive information.
Only two are rated Critical with a CVSS 3.1 base score of 9.8: CVE-2026-13684 in DSM's SCGI component, and CVE-2026-13639 in DSM's login logic. Both vectors have AV:N, AC:L, PR:N, UI:N — meaning they require no privileges and no user interaction to exploit over the network. The three entries that need no authentication should not be equated with "the two Critical ones": CVE-2026-13635 also needs no authentication, yet is rated only Moderate and lets an attacker obtain only non-sensitive information. The advisory's Mitigation field reads None.
The Fixed Release for Each Branch
The advisory's Affected Products table lists four release branches, with each fixed release written as "or above"; see the table below. Every row's Severity column reads Critical, which is the overall rating for that branch, not a claim that all eight CVEs are Critical. DSM 7.1, 7.0, and 6.2 are not listed in the table; for versions earlier than 7.2.1, the CVE records mark the status as unknown, not "not affected."
The DSM release notes date these four fixed releases between June 16 and July 29, 2026 — all earlier than the advisory's September 18 publication date. As checked against both sources through September 26, 2026, the official record does not explain why, and none is inferred here. In the release notes' Fixed Issues field, the three Update versions list fixes for a different advisory, Synology-SA-26:06; the security fixes listed for 7.4-90075 are Ghostscript's CVE-2023-43115 and "multiple security vulnerabilities" — neither names SA-26:13. It is the advisory that requires upgrading to these releases.
| Release branch | Fixed release required by the advisory | How the release notes phrase it, with date (last row is the CVE record) |
|---|---|---|
| DSM 7.4 | 7.4-90075 or above | 7.4-90075, June 16, 2026 |
| DSM 7.3 | 7.3.2-86009-4 or above | 7.3.2-86009 Update 4, July 29, 2026 |
| DSM 7.2.2 | 7.2.2-72806-9 or above | 7.2.2-72806 Update 9, June 30, 2026 |
| DSM 7.2.1 | 7.2.1-69057-12 or above | 7.2.1-69057 Update 12, June 30, 2026 |
| Versions earlier than DSM 7.2.1 | Not listed in the advisory | Both CVE records mark the status as unknown |
How to Check Your Own NAS
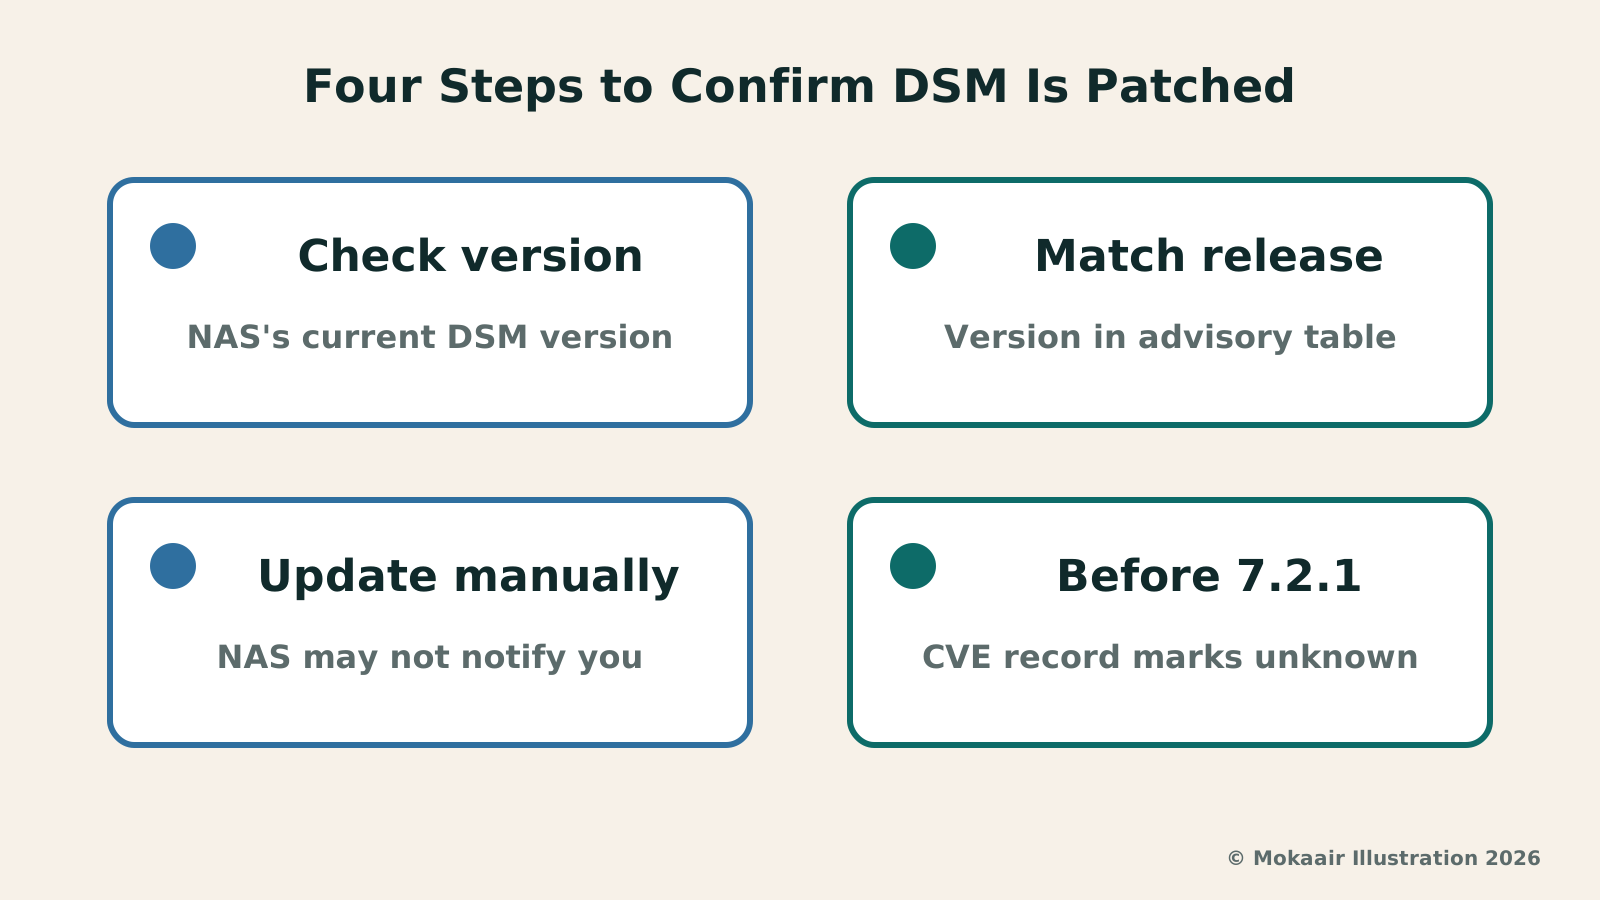
The first step in checking your own NAS is to look at your current DSM version number and compare it against the fixed release the advisory requires in the table above; none of the four sources state where in the interface to find the version number, so none is guessed here. The release notes for the three Update versions — DSM 7.3.2, 7.2.2, and 7.2.1 — state that the NAS may not notify you, either because the update has not yet reached your region or because the system has evaluated that no update is currently needed; not receiving a notification does not mean you are already on the fixed release.
Updating to any of the four fixed releases will restart the device. The 7.4-90075 release notes additionally state that if auto update does not run, you can perform a manual update in Control Panel, and that once this version is installed you cannot downgrade. For versions earlier than DSM 7.2.1, the advisory does not list them, and the CVE records mark the status as unknown; this advisory gives no answer for these versions.
The advisory itself provides no workaround beyond updating; the Mitigation field reads None (as checked on the advisory page through September 26, 2026). Neither the advisory nor the two CVE records state the number of affected devices, their regional distribution, or anything related to Taiwan.
What "Critical" and "No Known Exploitation" Mean
9.8 is the score Synology itself calculated using CVSS 3.1; the CNA (CVE Numbering Authority) for the CVE records is also Synology, and CISA did not assign a separate score in the CVE records. The CVSS 3.1 scores for the remaining six, in order, are: CVE-2026-13673 (Important, 8.8, LDAP API, requires authentication), CVE-2026-6205 (Important, 8.1, Upload API, requires authentication), CVE-2026-13635 (Moderate, 5.3, Auth API, no authentication required but only obtains non-sensitive information), CVE-2026-13623 (Moderate, 4.8, Theme API, requires administrator privileges), CVE-2026-13666 (Low, 3.5, Sharing API, requires authentication and requires the victim to click a sharing URL), and CVE-2026-13683 (Low, 2.7, EventScheduler API, requires administrator privileges).
CISA, acting as the ADP, added one SSVC assessment to each of the two CVE records, both timestamped in the early morning of September 19 Taipei time (still September 18 in US time): 3:14 AM for CVE-2026-13684 and 3:13 AM for CVE-2026-13639. All three fields are the same for both: Exploitation is none, Automatable is yes, and Technical Impact is total; neither had been updated again as of the September 26, 2026 check. These three values need to be read together — you cannot pick out just "none" and call it fine, nor can you flip it around and say for certain that no one has exploited it.
What's Still Unknown, and How to Check It Yourself
A few things could not be answered: the advisory does not state whether public exploit code or a proof of concept exists for these vulnerabilities; the Affected Products table lists only release branches, not affected models. The advisory also does not explain why its publication date is later than the fixed-release dates in the release notes, and no reason is inferred here.
What readers can check for themselves is going back to the SA-26:13 advisory page to see whether Last Updated and the Revision table have moved to Revision 2, or going back to the CVE-2026-13684 and CVE-2026-13639 records to see whether the three SSVC assessment values have changed. The status as of the September 26, 2026 check does not mean it will stay that way.
Frequently asked questions
My NAS hasn't shown an update notification — does that mean it's fine?
Not necessarily. The release notes for the three Update versions — DSM 7.3.2, 7.2.2, and 7.2.1 — state that the NAS may not show a notification because the update has not yet reached your region, or because the system has evaluated that no update is currently needed. Not receiving a notification does not mean you are already on the fixed release; you still need to check your DSM's current version number yourself against the four fixed releases the advisory requires.
I'm running DSM 7.1 or older — am I affected?
The advisory's Affected Products table does not list DSM 7.1, 7.0, or 6.2. For versions earlier than 7.2.1, both CVE records mark the status as unknown — not "not affected," and not "affected" either. As checked against this advisory and the two CVE records through September 26, 2026, no answer is given.
The advisory's Mitigation field reads None — what does that mean?
It means Synology has not provided any workaround other than updating in the advisory (as checked on the advisory page through September 26, 2026); the fix is to upgrade DSM to at least the fixed release the advisory lists.
Is there evidence these vulnerabilities have already been exploited?
CISA added one assessment to each of the two CVE records, timestamped in the early morning of September 19 Taipei time (September 18 US time); the Exploitation field (whether exploitation is known) reads none, and neither record had been updated as of the September 26, 2026 check. But the same assessment's Automatable is yes and Technical Impact is total; this is the assessment at that point in time, not a guarantee, and it does not mean no one has definitely exploited it.
Why are the fixed-release dates in the release notes earlier than the advisory's date?
The four fixed releases the advisory lists are dated between June 16 and July 29, 2026 in the DSM release notes, which is indeed earlier than the advisory's September 18 publication date. As checked against the advisory and the DSM release notes through September 26, 2026, neither explains why.
Where are the two Critical vulnerabilities, specifically?
CVE-2026-13684 is in DSM's SCGI component, and CVE-2026-13639 is in DSM's login logic. Both have a CVSS 3.1 base score of 9.8, and both vectors require no privileges and no user interaction, and can be exploited over the network — potentially letting a remote attacker read or write arbitrary files and cause denial of service. The advisory does not further explain the attack method, and no mechanism details are explained here either.
2026 Tech News Roundup: Key Points on Hardware, Platforms, Telecom, and Regulation2026 Tech News Roundup: Key Points on Hardware, Platforms, Telecom, and RegulationThis site's 2026 tech-news explainers in five groups — hardware, platforms, computing infrastructure, Taiwan policy, EU regulation: iPhone Duo and September hardware, M6/M5 Ultra, Snapdragon 8 Elite Gen 6, Project Zenith, Pixel Drop, App Store subscriptions, WordPress and Synology patches, NVIDIA, 6G, the Taiwan–Matsu cables, the sovereign AI corpus, the Cyber Resilience Act, the KIDS Act and Apple's EU terms. No purchase advice; vendor claims attributed; official sources and check dates.Read the full article
EU Cyber Resilience Act Reporting Obligations Begin September 11: Who Must Report, How FastEU Cyber Resilience Act Reporting Obligations Begin September 11: Who Must Report, How FastOn September 11, 2026, the reporting obligations under Article 14 of the EU's Cyber Resilience Act took effect, and ENISA launched its Single Reporting Platform. Based on the European Commission's reporting page, ENISA's press release and FAQ, and the Regulation's text in the Official Journal, this article explains how fast manufacturers must report, where reports go, which obligations already apply, which wait until December 2027, and the fine ceiling in Article 64.Read the full article
Found this guide helpful? Share it with someone who needs it
WordPress 7.1.2 Patches a Critical Core Vulnerability: Patched Versions by Branch and How to Check Your Site
On September 22, 2026, WordPress released 7.1.2, a security release patching a core vulnerability it rates as critical severity; the patch reaches back from the current 7.1 branch to the 4.7 branch. On September 25 (US time), CISA added it to its Known Exploited Vulnerabilities catalog based on evidence of active exploitation. This piece lays out the patched version for each branch and how to check your own site's version number (verified September 2026).
Qualcomm Unveils Two Snapdragon Flagship Mobile Platforms: How the Extreme and 8 Elite Gen 6 Differ
NVIDIA and Microsoft at Ignite: Vera Rubin NVL72 in Preview on Azure, Nemotron 3.5 in Foundry, Windows 365 Direct Stream in Limited Preview
Google Quantum AI Makes the Cover of Science: Quantum Contextuality Holds at Up to 105 Qubits, With a 98.3% Win Rate in a Coordination Game
Articles that cite this one
Sources
- Synology-SA-26:13 DSMChecked:
- CVE-2026-13684 (CVE record: CNA is Synology, includes the CISA ADP Vulnrichment assessment)Checked:
- CVE-2026-13639 (CVE record: CNA is Synology, includes the CISA ADP Vulnrichment assessment)Checked:
- Release Notes for DSM (the official data loaded by the DSM release notes page, en-global)Checked:
Compiled from the references and verification dates listed above; fares, schedules, product features, and terms can change, so please confirm the latest details on the relevant official website before travelling, booking, or purchasing.